How to Handle Bridging Aggregator Blacklists
 by
How to Handle Bridging Aggregator Blacklists: A Step-by-Step Recovery Guide
Knowing how to handle bridging aggregator blacklists starts with identifying why the block occurred and separating temporary technical issues from policy or trust-related problems. Bridging aggregators serve as critical connective hubs across modern digital infrastructure. They bind together diverse APIs, data streams, payment rails, affiliate networks, and cross-chain or multi-platform routing protocols. When an aggregator places your IP address, API key, domain, or account on a blacklist, the downstream impact can be severe. Traffic drops immediately, integrations break, referral chains rupture, and revenue streams halt.
For many operators, the knee-jerk reaction is to immediately file an appeal or submit a removal request pleading for reinstatement. However, simply requesting removal without resolving the root cause is rarely effective. Aggregators enforce strict algorithmic and manual filtering to protect their ecosystems from spam, security threats, network congestion, and malicious exploit attempts. If you request delisting while your system is actively throwing errors or flooding their endpoints with malformed traffic, your request will be rejected, or worse, your block will be escalated from a temporary suspension to a permanent ban.
Recovering from a blacklist requires a structured, diagnostic approach. This comprehensive guide details how to confirm a blacklist status, uncover the root cause, fix underlying infrastructure issues, prepare detailed documentation, submit a successful delisting request, and build long-term safeguards against future restrictions.
What Is a Bridging Aggregator Blacklist?
Before attempting recovery, it is essential to understand the underlying mechanics of a bridging aggregator and why these systems implement strict filtering controls.
What Is a Bridging Aggregator?
A bridging aggregator is an intermediary service or protocol designed to collect, normalize, route, and execute requests across multiple external platforms, feeds, networks, or databases. Instead of an end-user or system connecting individually to dozens of different endpoints, the bridging aggregator sits in the middle, functioning as a high-throughput router and liquidity or data broker.
These aggregators operate across various tech sectors:
-
Blockchain and DeFi: Cross-chain bridging aggregators route liquidity and token swaps across disparate blockchain networks.
-
AdTech and Affiliate Marketing: Data and referral aggregators route user impressions, clicks, and conversion data between advertisers, publishers, and affiliate networks.
-
E-Commerce and Supply Chain: Inventory and price aggregators pull real-time feed updates from vendor databases to serve downstream marketplaces.
-
API Gateways and Messaging: Communications aggregators route webhooks, SMS messages, and transactional notifications across global carriers.
Because bridging aggregators handle massive, multi-directional throughput, they are highly sensitive to abuse, malformed payloads, rate-limit violations, and malicious traffic.
What Does a Blacklist Mean?
A blacklist is an operational filter implemented by an aggregator to restrict access to its network, API, or protocol. Depending on the architecture of the aggregator, a blacklist can occur at several different levels:
-
IP-Level Blocking: The aggregator drops all incoming packets originating from a specific IP address or entire CIDR subnet at the firewall or gateway level.
-
Domain/Origin-Level Blocking: Requests containing specific cross-origin headers, domain names, or endpoint callbacks are blocked.
-
Account or API Key Revocation: Access tokens, partner IDs, or developer accounts are suspended, rendering all authenticated requests invalid.
-
Smart Contract / Address-Level Blocking: In decentralized protocols, wallet addresses or smart contract interactions are flagged and rejected by relayer networks or frontend interfaces.
Blacklists range from automated, temporary cooldowns to manual, permanent account terminations. It is critical to distinguish a true blacklist from standard rate limiting, temporary server downtime, or authentication credential expiration.
Why Blacklisting Happens
Aggregators enforce blacklists primarily to defend network integrity, system performance, and legal compliance. The most common drivers of blacklisting include:
-
Spam and Abusive Traffic Patterns: Submitting excessive, redundant, or rapid-fire requests that strain the aggregator’s infrastructure.
-
Security Vulnerabilities and Compromise: Exploited servers, compromised API credentials, or hijacked nodes broadcasting unauthorized traffic.
-
Data Quality and Policy Violations: Submitting duplicate items, fraudulent referral clicks, manipulated pricing feeds, or prohibited content.
-
Network Misconfigurations: Poorly coded integration loops, failing retry mechanisms, or misconfigured webhooks acting like a Denial of Service (DoS) attack.
-
Reputation Issues: Utilizing public hosting or shared IP pools that carry negative historical security scores or malicious association.
Step 1 — Confirm That You Are Actually Blacklisted
Before taking corrective action, you must verify that you are facing a true aggregator blacklist rather than a routine network disruption, localized outage, or software bug. Understanding how to handle bridging aggregator blacklists requires establishing clear diagnostic confirmation first.
Check the Error or Response
Analyze the raw HTTP response headers, API payload returns, or network logs generated when your system attempts to communicate with the bridging aggregator. Look for specific indicators:
-
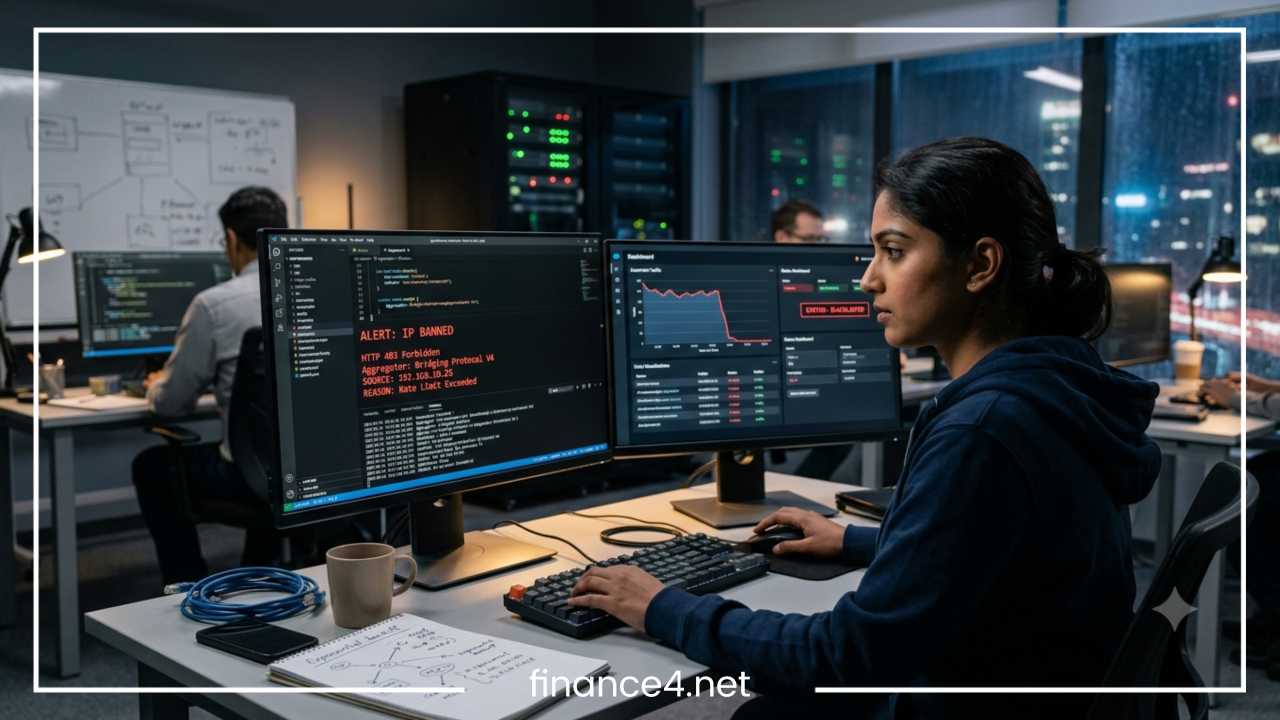
HTTP Status Codes: Look for HTTP 403 Forbidden, HTTP 401 Unauthorized, HTTP 429 Too Many Requests, or HTTP 502/503 Service Unavailable returned specifically from the aggregator’s security gateway (such as Cloudflare, AWS WAF, or Fastly).
-
Verbose Error Messages: Look for explicit responses such as “IP address banned,” “Access denied by security policy,” “Account suspended,” or “Invalid origin header.”
-
Connection Timeouts: A sudden shift from rapid API responses to complete packet drops (such as ETIMEDOUT or ECONNREFUSED) often indicates a firewall-level IP ban.
Determine the Scope of the Block
Isolate the exact boundaries of the restriction to narrow down your investigation. Run systematically controlled diagnostic tests to answer these questions:
-
Is it limited to a single IP address? Route a test request through an alternative static IP or off-network server. If the connection succeeds, the block is isolated to your primary IP address.
-
Is it tied to a specific API key or account? Execute an unauthenticated request or use a secondary sandbox API key from the same IP. If it succeeds, your primary API credentials have been flagged or suspended.
-
Is it domain or origin-specific? Send a request with altered origin headers or test from a secondary domain to check for origin filtering.
-
Are all endpoints affected? Check whether high-volume endpoints are blocked while lower-tier health check endpoints remain responsive.
Check Whether the Problem Is Temporary
Not every connection drop is a permanent blacklist. Aggregators frequently employ automated rate-limiting tiers. For example, exceeding a rate threshold might result in a 15-minute or 1-hour automated cooling-off period.
If you immediately begin submitting support tickets during a temporary 15-minute rate-limit window, you consume support bandwidth and risk drawing manual scrutiny to an issue that would have automatically resolved. Halt outbound automated scripts for a brief period, verify aggregator status pages, and check community support channels for broader network outages before concluding that a permanent blacklist is in place.
Step 2 — Identify the Reason for the Blacklist
Once a blacklist is confirmed, you must determine why your system triggered the restriction. Submitting an appeal without understanding the cause will lead to immediate rejection.
Review the Aggregator’s Policies
Reread the bridging aggregator’s official documentation, Acceptable Use Policy (AUP), Terms of Service (ToS), and developer guidelines. Take note of explicit parameters regarding:
-
Maximum allowable requests per second/minute (RPS/RPM).
-
Rules on concurrent websocket connections.
-
Payload size restrictions and formatting criteria.
-
Requirements for user-agent identification and custom request headers.
-
Rules regarding data scraping, re-aggregation, or automated arbitrage.
Examine Recent Infrastructure and Code Changes
System changes often trigger security filters. Review your internal version control and deployment history to establish a timeline of changes made right before the block occurred. Check whether your team recently migrated hosting providers, changed public IP blocks, introduced new automated cron jobs, updated webhook endpoints, or increased batch processing volume.
Look for Signs of Security Compromise
A sudden blacklist can be the first indication that your systems have been breached. If an unauthorized third party gains access to your server, API keys, or database, they may use your infrastructure to relay malicious traffic or launch attacks against third-party aggregators.
Perform an immediate security audit:
-
Inspect server processes for unauthorized execution scripts or web shells.
-
Audit API key usage logs for calls originating from unfamiliar geographic locations.
-
Check outbound firewall logs for abnormal traffic spikes originating from internal systems.
-
Verify whether system credentials, private keys, or secret tokens were exposed in public repositories.
Separate Cause From Correlation
Be careful not to confuse coincidental events with the root cause of the blacklist. For instance, if your system migrated to a new IP address hours before being blacklisted, the IP change itself might not be the issue; instead, the new IP address may have carried a poor reputation from its previous owner. Alternatively, the migration script may have introduced a bug that flooded the aggregator. Establish a clear, chronological sequence of events based on hard log data rather than assumptions.
Step 3 — Audit Your Traffic, Requests, and Integrations
To locate the exact technical trigger, you must perform a granular audit of your outgoing network traffic and integration scripts.
Review Application and Gateway Logs
Examine server access and application logs covering the 48 to 72 hours leading up to the blacklisting event. Aggregate your log data to analyze request distributions:
-
Calculate total request counts per minute and identify sudden spikes.
-
Track the percentage of successful HTTP 2xx responses versus failed HTTP 4xx or 5xx responses.
-
Group outbound calls by endpoint to identify specific endpoints experiencing heavy load.
-
Filter for repeated authentication failures, which often trigger security firewalls.
Examine Automation and Script Behavior
Automated processes are the leading cause of unintentional aggregator blocks. Audit all active automation routines:
-
Cron Jobs: Check if multiple scheduled tasks execute concurrently, creating massive, localized traffic spikes on the top of the hour.
-
Retry Mechanisms: Verify whether your code implements exponential backoff with jitter. Aggressive retries without backoff can turn a temporary network hiccup into a massive self-inflicted DoS attack.
-
Webhooks and Event Listeners: Ensure your handlers do not create infinite loop conditions, where receiving a payload automatically triggers an immediate response back to the aggregator.
Check for Duplicate or Malformed Requests
Integrations that submit corrupted, unformatted, or duplicate data feeds quickly trigger anti-spam filters. Audit payload logs for:
-
Repeated submission of identical transaction or data payloads.
-
Missing mandatory fields or improperly formatted JSON/XML payloads.
-
Incorrect encoding or broken character sets.
-
Invalid or expired authorization headers sent repeatedly within short timeframes.
Compare Normal vs. Abnormal Activity
Establish a baseline by comparing normal operational metrics against the anomaly window that triggered the blacklist.
| Audit Category | Baseline (Normal Pattern) | Anomaly Pattern (Trigger Event) |
| Request Volume | 500 requests per minute | 12,000 requests per minute |
| Error Rate | Below 0.5 percent failed responses | Over 45 percent authentication failures |
| Concurrency | 5 concurrent connections | 150 parallel websocket streams |
| Retry Behavior | Exponential backoff (3 retries) | Continuous loop without delay |
| Traffic Source | Single static gateway IP | Multiple unauthorized subnets |
Step 4 — Fix the Underlying Problem Before Requesting Removal
Attempting to contact the aggregator before resolving internal issues is a critical mistake. If the aggregator inspects your endpoints and finds active policy violations or abusive traffic patterns, your delisting request will be immediately denied.
Remediation for Excessive Traffic and Rate Violations
If your audit reveals rate limit breaches or excessive request volume:
-
Implement Caching Protocols: Cache static or slowly changing aggregator data locally using Redis or Memcached to drastically reduce outbound request counts.
-
Apply Rate Limiters Internally: Enforce strict internal queue systems (such as leaky bucket or token bucket algorithms) to cap outbound calls below the aggregator’s published limits.
-
Optimize Polling via Webhooks: Replace high-frequency HTTP polling mechanisms with WebSockets or webhooks where supported by the aggregator.
-
Refactor Retry Logic: Update integration scripts to use exponential backoff algorithms with randomized jitter to spread out reconnection attempts.
Remediation for Spam or Low-Quality Data Submissions
If the block stems from poor data quality, bad payloads, or duplicate content:
-
Purge Invalid Records: Clean your database and drop broken, corrupted, or duplicate data queues.
-
Strengthen Input Validation: Implement strict schema validation on your application layer to sanitize all data before it is transmitted to the aggregator.
-
Throttle Automated Publishing: Slow down batch processing routines to maintain steady data flow over time rather than processing massive bursts.
Remediation for Security Incidents and Compromise
If a security breach occurred:
-
Rotate All Credentials: Revoke existing API keys, access tokens, webhook secrets, and SSH keys immediately. Generate new, secure credentials.
-
Isolate Compromised Nodes: Quarantine affected virtual machines or containers, patch known vulnerabilities, and redeploy clean instances from verified code bases.
-
Implement IP Whitelisting: Restrict outgoing API calls so that only designated, secured internal server IPs can communicate with the aggregator.
Remediation for Configuration Errors
If a technical error or misconfiguration caused the block:
-
Fix broken DNS settings, update obsolete SSL/TLS certificates, and correct misconfigured API route paths.
-
Ensure all HTTP request headers comply strictly with the aggregator’s requirements (including accurate User-Agent, Content-Type, and Accept headers).
Step 5 — Document Everything Before Contacting the Aggregator
When you reach out to an aggregator’s abuse or engineering team, you must present a professional, clear, and well-documented case. Aggregator support teams handle high ticket volumes; concise, evidence-backed requests are prioritized over vague complaints.
Key Evidence to Compile
Gather all technical facts into a single diagnostic document before writing your appeal:
-
Identification Details: Account ID, primary domain, affected IP addresses, API key IDs (never include private secrets or passwords), and public wallet addresses if applicable.
-
Incident Timeline: Precise timestamp (in UTC) when the issue was first detected, alongside timestamps of your internal code deployments or server events.
-
Root Cause Analysis: A brief, clear explanation of exactly what failed, backed by error logs and audit metrics.
-
Remediation Steps Taken: Explicit proof of code fixes, configuration updates, security patches, or queue implementation.
-
Preventive Safeguards: Details on new monitoring, rate-limiting rules, or alerting mechanisms deployed to prevent recurrence.
What NOT to Do When Documenting and Appealing
Avoid common tactical missteps that negatively impact your standing:
-
Do not file multiple support tickets: Submitting duplicate tickets across email, Discord, Telegram, and web forms fragments support communication and creates delays.
-
Do not use emotional language: Avoid complaining about financial loss, threatening legal action, or blaming the aggregator’s systems.
-
Do not bypass the block using unauthorized workarounds: Rapidly spinning up new proxy IPs or creating burner accounts to circumvent a ban shows bad faith and usually results in permanent blacklisting of your entire domain or business entity.
Step 6 — Submit a Blacklist Removal Request
With your systems fixed and documentation organized, you are ready to submit an appeal.
Structuring the Removal Request
Format your appeal professionally. The structure below provides an effective blueprint for an aggregator delisting request:
Section 1: Affected Identifiers Include your domain (e.g., example.com), affected IP address (e.g., 192.0.2.45), and Account ID (e.g., ACC-89231).
Section 2: Incident Overview State the exact date and UTC time when HTTP 403 errors were observed. Explain the technical root cause clearly, such as a software deployment triggering an uncaught retry loop that caused abnormal request volume violating rate limits.
Section 3: Corrective Actions Taken List the exact technical remediations deployed, including the software version release, client-side rate limits applied (such as capping at 50 requests per second), and addition of exponential backoff and Redis caching.
Section 4: Prevention Safeguards Describe automated monitoring deployed to halt outbound requests if error rates exceed 2 percent.
Section 5: Request and Evidence Formally ask for a review and delisting of the affected IP, domain, or account, and attach normalized log samples for verification.
Keep the Request Factual and Direct
Keep your explanation short and focused on technical data. State what happened, demonstrate that it has been fixed, and prove that it will not happen again. Abuse teams handle dozens of appeals daily; they look for technical competency, accountability, and clear evidence of remediation.
When and How to Follow Up
Response times vary depending on the aggregator’s team size, support structure, and severity tier.
-
Standard API/SaaS Aggregators: Allow 24 to 48 hours before sending a follow-up inquiry.
-
Decentralized / Community Protocols: Check official developer channels (such as dedicated Discord support tiers or governance forums) for clear appeal guidelines.
-
When Following Up: Reply directly within the original support thread. State clearly that you are checking on the status of your ticket ID and confirm that your systems remain clean and monitored.
Step 7 — Monitor the Delisting and Recovery Process
Receiving notification that your blacklist entry has been removed is an important milestone, but the recovery process is not complete. You must manage the restoration of network traffic carefully.
Controlled Traffic Ramping
If your infrastructure was blacklisted due to traffic volume, do not immediately switch 100 percent of your production load back to the aggregator. Aggregator security filters dynamically score incoming IP and domain reputation. A sudden jump from zero to millions of requests can instantly trigger automated security controls, landing your system back on the blacklist.
Gradually scale your integration traffic back up using a phased approach:
| Recovery Phase | Timeframe | Action | Verification |
| Phase 1 | Hours 1 to 4 | Restore 10 percent of traffic | Monitor error rates |
| Phase 2 | Hours 4 to 12 | Scale to 25 percent of traffic | Verify latency and rate limits |
| Phase 3 | Hours 12 to 24 | Scale to 50 percent of traffic | Check gateway logs |
| Phase 4 | Hours 24 to 48 | Scale to 100 percent of traffic | Full system operational |
Monitor Real-Time Diagnostics
During the first 72 hours after reinstatement, closely monitor key health metrics:
-
HTTP Status Distribution: Confirm that success rates remain near 100 percent and that HTTP 403 or HTTP 429 responses remain at zero.
-
Latency Benchmarks: Watch for elevated response times, which can indicate that your traffic is passing through secondary inspection or scrubbing layers.
-
System Log Alerts: Set up real-time alerts for any unexpected spike in connection failures or authentication errors.
Step 8 — Prevent Future Bridging Aggregator Blacklists
Long-term stability requires shifting from reactive recovery to proactive prevention. Build technical safeguards directly into your pipeline to protect your infrastructure from repeated blacklisting.
Establish Continuous Monitoring and Rate Limiting
Do not rely solely on the aggregator to enforce traffic boundaries. Control your outgoing traffic internally:
-
Enforce Local Rate Governors: Implement internal rate limiting using software middleware to ensure outgoing requests stay well below published aggregator thresholds.
-
Circuit Breakers: Implement structural design patterns like the Circuit Breaker pattern. If your application detects a sudden spike in HTTP 4xx or 5xx errors from the aggregator, the circuit breaker trips—automatically pausing all outgoing calls for a set duration rather than continuing to bombard the failing endpoint.
Implement Real-Time Alerting
Configure automated monitoring systems (such as Prometheus, Datadog, or Grafana) to alert your engineering team before issues escalate into blacklists:
-
Traffic Anomaly Alerts: Trigger alerts if outbound API request rates increase by more than 30 percent over baseline within a 5-minute window.
-
Error Rate Thresholds: Set high-priority alerts if HTTP 429 Too Many Requests or HTTP 403 Forbidden responses exceed 1 percent of total outgoing traffic.
-
Credential Expiration Tracking: Automate alerts 30 days prior to SSL certificate or API key expirations.
Maintain Healthy API Integration Practices
Adopt strict integration lifecycle policies across your organization:
-
Rotate Keys Safely: When updating API keys, maintain overlapping validity periods so systems can transition smoothly without authentication drops.
-
Sandbox Testing: Never test new scripts, scrapers, or automation routines directly against live aggregator production endpoints. Conduct all testing inside staging or sandbox environments.
-
Audit Third-Party Dependencies: Regularly audit software libraries and integrations to ensure they are updated, secure, and fully compliant with current aggregator standards.
Common Mistakes When Handling Aggregator Blacklists
Avoiding these common pitfalls will save time and protect your reputation during the recovery process:
-
Assuming every connection failure is a blacklist: Sending angry support emails during a brief service outage damages your relationship with the aggregator’s support team. Validate logs, test alternative IPs, and check network status pages before assuming you are blacklisted.
-
Submitting an appeal before fixing the root cause: Aggregators will check your live traffic upon receiving your appeal. If the issue is still active, your request will be immediately rejected. Fully audit logs, patch software bugs, enforce internal rate limits, and verify system stability before sending a delisting request.
-
Trying to bypass the blacklist using proxies or secondary accounts: Aggregators detect evasion tactics easily. Circumventing blocks often converts a temporary IP restriction into a permanent ban on your main domain, business identity, or wallet contracts. Address the problem directly through official appeal channels with transparent documentation.
-
Using aggressive, demanding, or emotional language in support tickets: Unprofessional communication lowers the priority of your ticket and alienates support engineers. Keep all communications polite, concise, professional, and grounded entirely in technical facts.
-
Restoring 100 percent of production traffic immediately after removal: A sudden surge of high-volume traffic can trigger automated security thresholds, placing your IP straight back on the blacklist. Ramp up traffic in controlled phases while closely monitoring real-time error rates.
Practical Bridging Aggregator Blacklist Recovery Checklist
Use this checklist to track your recovery process step by step.
Stage 1: Diagnosis & Scoping
-
Confirm the block using raw HTTP status codes, error payloads, and network logs.
-
Test alternative IPs, API keys, and domains to determine the exact scope of the block.
-
Verify that the issue is not a temporary local outage, DNS issue, or scheduled aggregator maintenance.
Stage 2: Audit & Root Cause Analysis
-
Audit outbound application and gateway logs for traffic spikes, loop conditions, or high error rates.
-
Review recent software deployments, infrastructure migrations, and cron job configurations.
-
Conduct a thorough security scan to rule out credential theft, malicious activity, or system compromise.
Stage 3: System Remediation
-
Patch software bugs, fix broken retry loops, and implement exponential backoff algorithms.
-
Configure internal rate-limiting controls and caching layers (e.g., Redis).
-
Rotate all API keys, access tokens, and passwords if security was compromised.
Stage 4: Documentation & Appeal
-
Compile incident data: affected identifiers, precise UTC timestamps, root cause explanation, and proof of fixes.
-
Draft a clear, polite, and technical delisting appeal.
-
Submit the appeal through official support channels and refrain from filing duplicate tickets.
Stage 5: Restoration & Prevention
-
Upon delisting, gradually ramp production traffic back up in controlled phases.
-
Deploy automated circuit breakers and local rate governors.
-
Set up real-time monitoring alerts for traffic spikes and HTTP 4xx or 5xx error thresholds.
Conclusion
Knowing how to handle bridging aggregator blacklists comes down to a structured process of diagnosis, technical remediation, and clear communication. A blacklist is an automated or manual defense mechanism designed to protect system stability and network integrity. Treating it as an engineering diagnostic task rather than an administrative dispute is the key to swift reinstatement.
When a block occurs, resist the urge to immediately send an unprepared appeal or bypass security filters. Take time to systematically confirm the restriction, audit outbound logs, fix underlying software or security issues, and document your corrective actions. Presenting a factual, evidence-backed appeal demonstrates technical competency and accountability—making it easy for the aggregator’s team to approve your request.
Once reinstated, focus on prevention. By implementing local rate governors, circuit breaker patterns, automated traffic alerts, and regular security audits, you build resilient infrastructure that keeps your integrations running smoothly without triggering aggregator security filters.
Frequently Asked Questions (FAQ)
What is the fastest way to check if an API key or IP address is blacklisted by an aggregator?
To determine if you are facing an IP ban or API key revocation, isolate your request environment. Run a curl command or API request from your primary server, then repeat the exact test using a clean, alternative static IP address and a secondary sandbox API key. If the request succeeds over the alternative IP, your primary server IP is blocked at the firewall level. If the request returns HTTP 403 Forbidden or HTTP 401 Unauthorized regardless of IP, your API key or account status has been suspended.
Why does my API integration keep getting HTTP 429 Too Many Requests errors?
An HTTP 429 Too Many Requests status code indicates that your system has exceeded the bridging aggregator’s rate limit policy (Requests Per Second or Requests Per Minute). This typically happens due to un-cached polling routines, overlapping cron jobs running simultaneously, or retry mechanisms without exponential backoff. While an HTTP 429 is often a temporary automated cooldown, continuously ignoring rate limits can escalate your status to a permanent HTTP 403 IP or domain blacklist.
Should I use proxy IPs to bypass an active bridging aggregator blacklist?
No. Using proxy pools, rotating residential IPs, or spinning up burner accounts to bypass an active blacklist is considered an evasion tactic. Aggregators deploy security filters, fingerprinting tools, and behavior analysis to detect circumvented traffic. If an aggregator identifies evasion attempts, they will likely escalate a temporary IP suspension into a permanent, non-negotiable domain, brand, or smart contract blacklist.
How long does it take for a bridging aggregator to process a delisting appeal?
Unban appeal response times vary depending on the aggregator’s infrastructure and team size. Standard SaaS API aggregators typically respond within 24 to 48 business hours. Decentralized protocols or web3 cross-chain bridges may handle appeals through dedicated Discord ticket channels or governance forums, which can take anywhere from a few hours to several days. Always wait at least 48 hours before sending a polite follow-up in your original support thread.
What is the Circuit Breaker pattern, and how does it prevent API blacklisting?
The Circuit Breaker pattern is a software design structure that monitors outbound API requests for failure rates. If an external service or bridging aggregator starts returning elevated error rates (such as HTTP 429 or HTTP 5xx responses), the circuit breaker “trips” and temporarily stops all outbound application calls for a set period. This prevents your application from continuously hammering a struggling or rate-limiting endpoint, protecting your infrastructure from automated anti-spam bans.
How do I write a successful blacklist removal request to an API support team?
A successful appeal must be concise, professional, and backed by technical logs. Your appeal should clearly state:
-
The affected identifiers (IP, domain, account ID).
-
The exact UTC timestamp and root cause of the traffic anomaly.
-
The technical fixes deployed (such as rate governors, Redis caching, or exponential backoff).
-
The automated monitoring safeguards implemented to prevent a recurrence.
Avoid emotional explanations or submitting multiple duplicate tickets, as this delays support review.